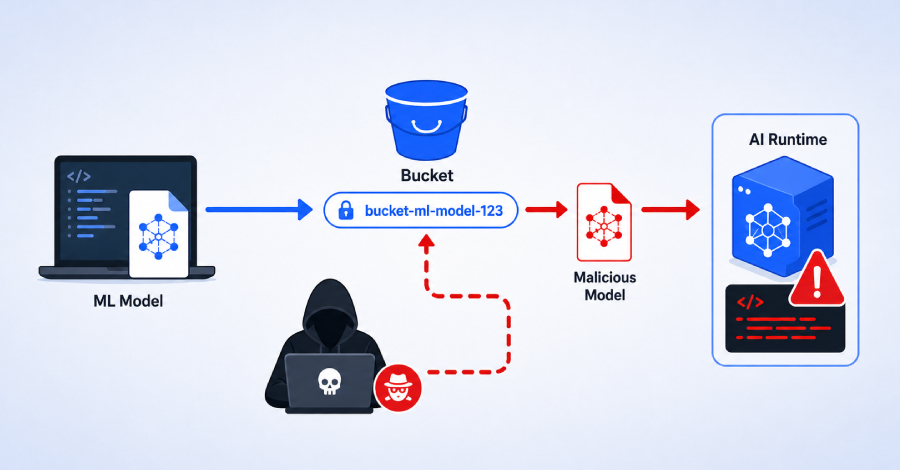
A race-condition vulnerability in the Google Cloud Vertex AI Python SDK allowed an attacker with only a public project ID to intercept model uploads and execute arbitrary code in Google's serving infrastructure. Palo Alto Networks Unit 42, which reported the bug via Google's bounty program, dubbed the attack "Pickle in the Middle." No exploitation in the wild has been observed, and Google patched the issue in SDK version 1.148.0.
The flaw lived in how the SDK selected a default Cloud Storage staging bucket for model uploads. When a user omitted the `staging_bucket` parameter, the SDK generated a deterministic bucket name from the project ID and region—e.g., `project-vertex-staging-region`. It checked if the bucket existed but never verified ownership. Since bucket names are globally unique, an attacker could pre-create that bucket in their own project. The victim's SDK would then upload model files to the attacker's bucket, where the attacker could swap the model with a malicious pickle or joblib file. When Vertex AI later loaded the swapped model, the attacker's code executed inside the serving container.
Timing was critical. Unit 42 measured a ~2.5-second window between upload and model loading. Their proof-of-concept used a Cloud Function triggered on upload to replace the model in 1.4 seconds. The payload exfiltrated an OAuth token from the container's metadata server. In their test environment, that token granted access to other model artifacts, BigQuery metadata, GKE cluster names, and internal container paths within the same Google-managed tenant project.
The attack required two conditions: the victim's default staging bucket didn't exist in that region (common for new Vertex AI projects), and the developer relied on the SDK default instead of specifying a bucket. Unit 42 reported the flaw on March 5, 2026. Google's initial fix (v1.144.0) added a random UUID to bucket names; the full fix (v1.148.0) added ownership verification. No CVE has been assigned.
Update to v1.148.0 or later, and always set an explicit `staging_bucket` you control. Check the SDK version in notebooks, CI jobs, and training pipelines—not just production services. This is the second predictable-bucket-name bug in Vertex AI this year, following CVE-2026-2473.
Source: The Hackers News