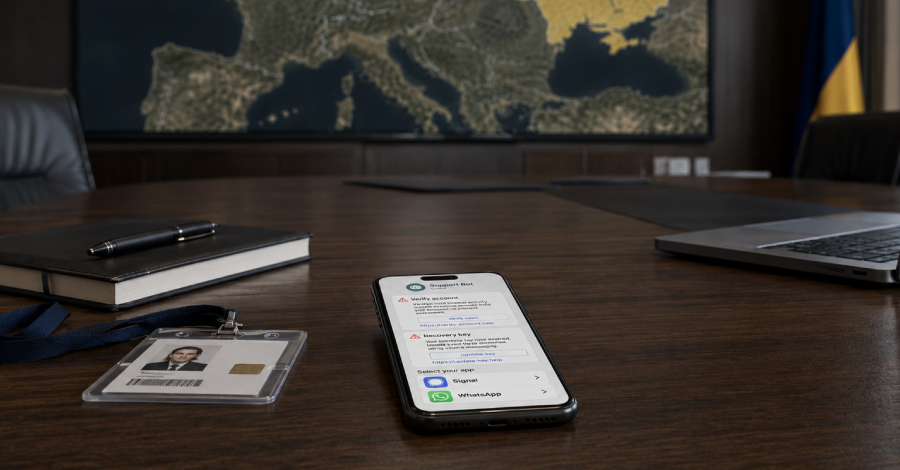
A joint investigation by the Security Service of Ukraine and the US Federal Bureau of Investigation has uncovered a sophisticated cyber campaign orchestrated by Russian intelligence services. The attackers have been using fake support texts to trick government officials, military personnel, politicians, and activists in Ukraine, Europe, and the US into divulging their messaging account credentials. The primary objective of these attacks is to gain unauthorized access to sensitive information, including military, political, and economic data, as well as personal user information. The SSU has warned that these attacks are not limited to organizations and public figures, but also target personal accounts of Ukrainian nationals. While the campaign has not been attributed to a specific hacking group, similar attacks on Signal and WhatsApp users have been linked to Russian threat activity clusters. To mitigate these threats, users are advised to regularly review their active messaging app sessions, enable two-factor authentication, and exercise caution when interacting with unknown users or links. This incident highlights the importance of robust security measures, including periodic session reviews and secure authentication protocols, to protect against phishing attacks. The FBI has also attributed Russian Intelligence Services to a commercial messaging application phishing campaign, emphasizing the need for vigilance in the face of evolving cyber threats.
Source: The Hackers News