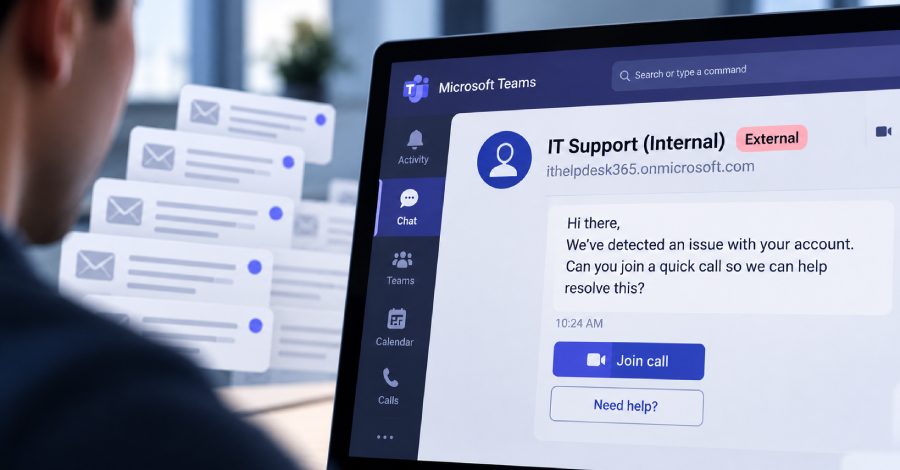
Threat actors are exploiting Microsoft Teams' external chat feature to impersonate IT support staff and deliver malware, including ransomware, according to a report from Arctic Wolf Labs shared with The Hacker News. Researchers describe a recurring social engineering pattern across hundreds of cases.
Attackers consistently use throwaway Microsoft 365 tenants with display names like "IT Support (Internal)," "Help Desk," and "IT Service Desk," sometimes adding the target company's name for credibility. Roughly 30-40% of investigated cases used *.onmicrosoft.com fallback domains with help desk-themed names. In many cases, victims are first hit with email bombing - floods of newsletter sign-ups - to create urgency before the Teams message arrives.
The activity aligns with STAC4749, a group linked to Chaos ransomware deployment, according to Sophos. Attackers use voice phishing to convince victims to grant remote access through legitimate tools such as Quick Assist, AnyDesk, ScreenConnect, TeamViewer, Atera, Zoho Assist, NetSupport, and LogMeIn. That access is then used for reconnaissance, payload delivery, lateral movement to domain controllers, data exfiltration, and ransomware deployment.
In one case, a victim was told to run a PowerShell command downloading an MSI installer from Azure Blob Storage, which launched a Python implant that queried Active Directory and sent data to an external server. Arctic Wolf noted attackers often avoid pasting URLs directly into Teams to evade Safe Links scanning, navigating to payloads themselves during remote sessions instead. "External Microsoft Teams chat has become an effective initial-access vector because it exploits trust rather than a software vulnerability," the firm said.
Source: The Hackers News