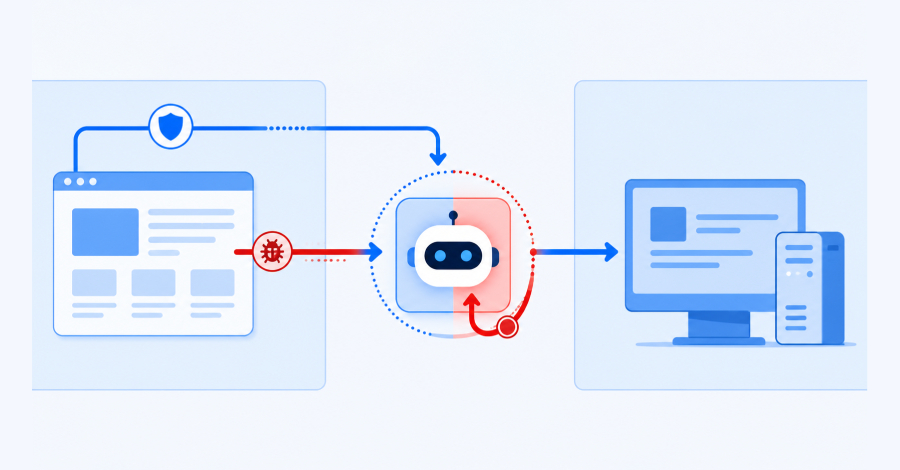
Microsoft researchers have identified a vulnerability in the AutoGen Studio framework, which allows an attacker to hijack an AI browsing agent and execute arbitrary code on the host machine. The exploit, dubbed AutoJack, relies on a combination of three weaknesses in the Model Context Protocol (MCP) WebSocket surface. Firstly, the socket trusts localhost, allowing a browsing agent running on the same machine to inherit this trust. Secondly, the authentication middleware skips MCP paths, assuming the handler will verify tokens itself. Finally, the endpoint takes a command straight from a request parameter and runs it without any allowlist or authentication. To mitigate this vulnerability, users who have installed pre-release builds 0.4.3.dev1 or 0.4.3.dev2 should pull the updated code from GitHub main at or after commit b047730. Alternatively, separating the pieces required for the attack, such as running AutoGen Studio on a separate machine or under a low-privilege account, can also prevent exploitation. The vulnerability highlights the importance of authenticating the control plane, keeping process execution behind an allowlist, and giving agents their own identity. Microsoft expects similar vulnerabilities to exist in other agent frameworks, emphasizing the need for robust security measures to prevent such attacks.
Source: The Hackers News